Day: December 25, 2022

  • Audit Risk

    Audit Risk

    Audit risk is the risk of expressing an inappropriate audit opinion on financial statements that are materially misstated.

    The objective of the audit is to reduce this audit risk to an acceptably low level.

    审计风险是指对有重大误报的财务报表发表不恰当的审计意见的风险。

    审计的目的是将这种审计风险降低到一个可接受的低水平。

    Audit risk has two key elements, as illustrated below.

    审计风险有两个关键因素,如下图所示。
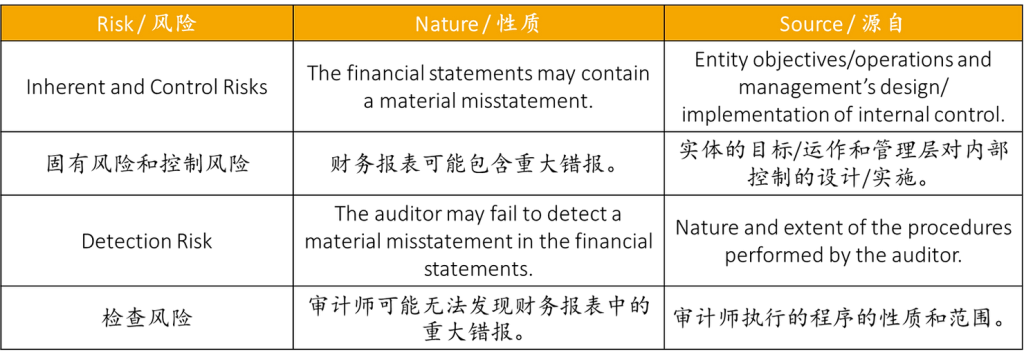
    To reduce audit risk to an acceptably low level, the auditor is required to:

    • Assess the risks of material misstatement; and
    • Limit detection risk. This may be achieved by performing procedures that respond to the assessed risks of material misstatement, both at the financial statement level and at the assertion level, for classes of transactions, account balances, and disclosures.

    为了将审计风险降低到可接受的低水平,审计师需要:

    • 评估重大错报的风险;以及
    • 限制检查风险。这可以通过执行程序来实现,以应对在财务报表层面和认定层面上对交易类别、账户余额和披露的重大错报风险的评估。

    Audit Risk Components | 审计风险成分

    Inherent Risk
    Description: The susceptibility of an assertion about a class of transaction, account balance, or disclosure to a misstatement that could be material, either individually or when aggregated with other misstatements, before consideration of any related controls.

    Commentary: This includes events or conditions (internal or external) that could result in a misstatement (error or fraud) in the financial statements.

    The sources of risk (often categorised as business or fraud risks) can arise from the entity’s objectives, the nature of its operations/industry, the regulatory environment in which it operates, and its size and complexity

    固有的风险
    描述: 在考虑任何相关的控制措施之前,关于某类交易、账户余额或披露的断言对错报的易感性,无论是单独还是与其他错报相加,都可能是重大的。

    评注: 这包括可能导致财务报表出现错报(错误或欺诈)的事件或条件(内部或外部)。

    风险的来源(通常被归类为商业或欺诈风险)可能来自于实体的目标、其业务/行业的性质、其运营的监管环境以及其规模和复杂性。

    Control Risk
    Description: The risk that a misstatement that could occur in an assertion about a class of transaction, account balance, or disclosure and that could be material, either individually or when aggregated with other misstatements, will not be prevented, or detected and corrected, on a timely basis by the entity’s internal control.

    Commentary: Management designs controls to mitigate a specified inherent (business or fraud) risk factor. An entity assesses its risks (risk assessment) and then designs and implements appropriate controls to reduce its risk exposure to a tolerable (acceptable) level.

    Controls may be:

    • Pervasive in nature, such as management’s attitude toward control, commitment to hiring competent people, and prevention of fraud. These controls are assessed at the financial statement level; and
    • Specific to the initiation, processing, or recording of a particular transaction. These are often called business process, activity-level, or transaction controls.

    控制风险
    描述: 在关于某类交易、账户余额或披露的认定 (Assertion) 中可能发生的错报,以及可能是重大的错报,无论是单独的还是与其他错报合计的,都不能被实体的内部控制所防止,或不能及时发现和纠正的风险。

    评注: 管理层设计控制以减轻特定的内在(业务或欺诈)风险因素。

    一个实体评估其风险(风险评估),然后设计并实施适当的控制,以将其风险暴露降低到可容忍(可接受)的水平。

    控制措施可以是:

    • 具有普遍性,如管理层对控制的态度,对雇用合格人员的承诺,以及对欺诈的预防。这些控制是在财务报表层面上进行评估的;以及
    • 具体到某项交易的启动、处理或记录。这些通常被称为业务流程、活动层面或交易控制。

    Detection Risk
    Description: The risk that the procedures performed by the auditor to reduce audit risk to an acceptably low level will not detect a misstatement that exists and that could be material, either individually or when aggregated with other misstatements.

    Commentary: The auditor assesses the risks of material misstatement (inherent and control risk) at the financial statement and assertion levels.

    Audit procedures are then developed to reduce audit risk to an acceptably low level.

    This includes consideration of the potential risk of:

    • Selecting an inappropriate audit procedure;
    • Misapplying an appropriate audit procedure; or
    • Misinterpreting the results from an audit procedure.

    检查风险
    描述:审计员为将审计风险降低到可接受的低水平而实施的程序不能发现存在的、可能是重大的、单独或与其他错报合在一起的错报的风险。

    评论:审计师在财务报表和认定层面评估重大错报的风险(固有的和控制的风险)。

    然后制定审计程序,将审计风险降低到一个可接受的低水平。这包括对以下潜在风险的考虑:

    • 选择一个不适当的审计程序。
    • 误用适当的审计程序;或
    • 误解审计程序的结果。

    Note: The ISAs define the risk of material misstatement at the assertion level as consisting of two components: inherent risk and control risk.
    Consequently, the ISAs do not ordinarily refer to inherent risk and control risk separately, but rather to a combined assessment of the “risks of material misstatement.”

    However, the auditor may make separate or combined assessments of inherent and control risk, depending on preferred audit techniques or methodologies and practical considerations.

    注:《国际审计准则》将认定层面的重大错报风险(risk of material misstatement, ROMM) 定义为由两部分组成:固有风险和控制风险。

    因此,《国际审计准则》通常不单独提及固有风险和控制风险,而是提及对 “重大错报风险 “的综合评估。然而,审计师可以对固有风险和控制风险进行单独或合并评估,这取决于首选的审计技术或方法以及实际考虑。

    CONSIDER POINT
    Separate business and fraud risks

    Many inherent risks can result in both business and fraud risks. For example, a new accounting system may create potential for errors (business risk), but may also provide an opportunity for someone to manipulate financial results or misappropriate funds (fraud risk).

    So when a business risk is identified always consider whether this also creates a fraud risk. If it does, record and assess the fraud risk separately from the business risk factors. Otherwise it is possible that the audit response will only address the business-risk element and not the fraud risk.

    Recording fraud risks

    Fraud is often identified through the examination of:

    • Unusual patterns, exceptions and oddities in transactions/events; or
    • Individual(s) with the motive, opportunity, and rationalization to commit fraud.

    If such matters are observed (during any stage of the audit) they should be recorded and assessed as fraud risks, even if they seem on the surface to be immaterial. Recording such risks will help ensure they are appropriately considered when developing the audit response.

    考虑要点
    分离业务和欺诈风险

    许多固有的风险可能导致商业和欺诈风险。例如,一个新的会计系统可能会产生潜在的错误(商业风险),但也可能为某人操纵财务结果或挪用资金提供机会(欺诈风险)。

    因此,当一个商业风险被确认时,一定要考虑这是否也会产生欺诈风险。

    如果是这样,就将欺诈风险与商业风险因素分开记录和评估。

    否则,审计反应有可能只涉及业务风险因素而不涉及欺诈风险。

    记录欺诈风险

    欺诈通常是通过检查来识别的:-

    • 交易/事件中的异常模式、例外情况和怪异现象;或
    • 具有实施欺诈的动机、机会和合理化的个人。

    如果发现这些问题(在审计的任何阶段),应将其作为欺诈风险进行记录和评估,即使它们表面上看起来并不重要。记录此类风险将有助于确保在制定审计对策时对其进行适当的考虑。

    Summary of the Audit Risk Components
    The following chart shows the interrelationship between risk and control.

    The inherent risk bar contains all the business and fraud risk factors that could result in the financial statements being materially misstated (before any consideration of internal control).

    The control risk bars reflect the pervasive and transactional control procedures put into effect by management to mitigate the risk that the financial statements are misstated.

    The extent to which the control risk bars do not completely mitigate the inherent risks is often called management’s residual risk, risk appetite or risk tolerance.

    审计风险组成部分的摘要

    下图显示了风险和控制之间的相互关系。

    固有风险栏包含了所有可能导致财务报表出现重大误报的商业和欺诈风险因素(在对内部控制进行任何考虑之前)。

    控制风险栏反映了管理层为减少财务报表被误报的风险而实施的普遍性和交易性控制程序。

    控制风险栏不能完全缓解固有风险的程度,通常被称为管理层的剩余风险、风险偏好或风险容忍度。

    Note: The length of the bars in the exhibit would vary based on the particular circumstances and risk profile of the entity.

    注:根据实体的特定情况和风险状况,展览中的条形长度会有所不同。

    The chart below outlines the auditor’s role in assessing the risks of material misstatement in the financial statements and then performing responsive audit procedures designed to reduce the audit risk to an appropriately low level.

    下图表概述了审计师在评估财务报表中的重大错报风险,然后执行旨在将审计风险降低到适当低水平的响应性审计程序中的作用。

    Note: The length of the bars in the exhibit would vary based on the particular circumstances and risk profile of the entity, and the nature of the auditor’s response.

    注:根据该实体的特定情况和风险状况以及审计师应对的性质,展览中的条形图的长度将有所不同。
    Our website's articles, templates, and material are solely for you to look over. Although we make every effort to keep the information up to date and accurate, we make no representations or warranties of any kind, either express or implied, regarding the website or the information, articles, templates, or related graphics that are contained on the website in terms of its completeness, accuracy, reliability, suitability, or availability. Therefore, any reliance on such information is strictly at your own risk.

    Keep in touch with us so that you can receive timely updates |

    要获得即时更新,请与我们保持联系

    1. Website ✍️ https://www.ccs-co.com/ 2. Telegram ✍️ http://bit.ly/YourAuditor 3. Facebook ✍

    4. Blog ✍ https://lnkd.in/e-Pu8_G 5. Google ✍ https://lnkd.in/ehZE6mxy

    6. LinkedIn ✍ https://www.linkedin.com/company/74734209/admin/
    13
  • How to Perform a Risk-Based Audit

    How to Perform a Risk-Based Audit

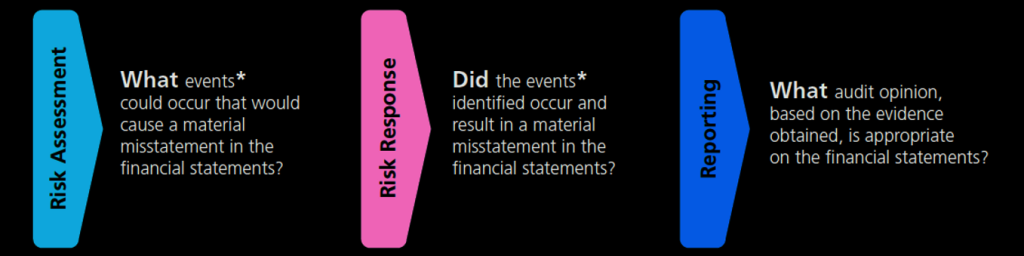
    A risk-based audit has three key steps, as illustrated below.

    Risk Assessment

    Description: Performing risk assessment procedures to identify and assess the risks of material misstatement in the financial statements.

    This includes the assessment of significant risks, control deficiencies and identified or suspected non-compliance with laws and regulations that will be addressed in the audit and communicated to Those charged with governance (TCWG).

    The auditor would also select Key Audit Matters (KAM) for inclusion in the auditor’s report for listed entities and for all audits where ISA 701, related to key audit matters, is to be applied as required by local law, regulation or voluntarily.

    Risk Response

    Description: Designing and performing further audit procedures that respond to identified and assessed risks of material misstatement, at both the financial statement and assertion levels.

    Reporting

    Description: This involves:

    • Forming an opinion based on the audit evidence obtained and the evaluation of the financial statement presentation and disclosures; and
    • Preparing and issuing a report that is appropriate to the conclusions reached.

    基于风险的审计有三个关键步骤,如下所示:

    风险评估

    描述:执行风险评估程序以识别和评估财务报表中的重大错报风险。

    这包括评估重大风险、控制缺陷和已发现或怀疑的不符合法律和法规的情况,这些问题将在审计中得到解决并传达给负责管理的人。

    审计师还将选择关键审计事项 [Key Audit Matters (KAM)] 纳入上市实体的审计报告,以及根据当地法律、法规的要求或自愿采用与关键审计事项相关的 ISA 701 的所有审计。

    风险应对

    描述:设计和执行进一步的审计程序,以应对在财务报表和断言层面上已确定和评估的重大错报风险。

    报告

    描述:这包括:-

    • 根据所获得的审计证据以及对财务报表列报和披露的评价形成意见;以及
    • 编制并发布一份与所得出的结论相适应的报告。

    A simple way of describing the three elements is illustrated below.

    下面是描述这三个要素的一个简单方法。

    * an “event” is simply a business or fraud risk factor. This would also include risks resulting from the absence of internal control to mitigate the potential for material misstatements in the financial statements.

    * 一个 “事件 “只是一个商业或欺诈风险因素。这也包括因缺乏内部控制以减少财务报表中重大错报的可能性而导致的风险。

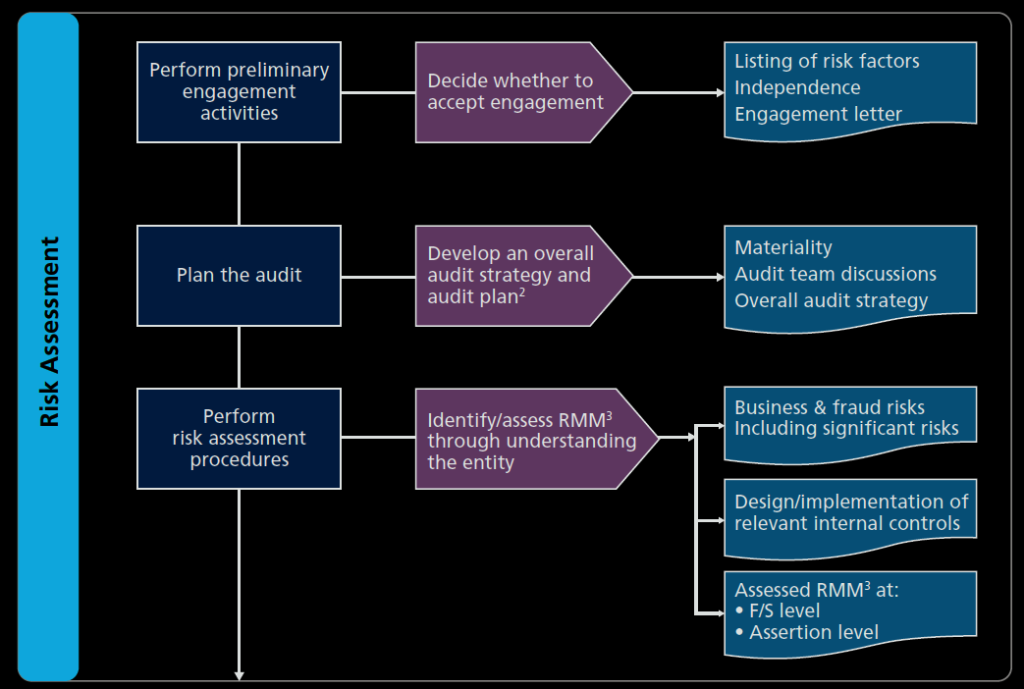
    The various tasks involved in each of these three phases are outlined below.

    这三个阶段中每个阶段所涉及的各种任务概述如下。

    Risk Assessment | 风险评估

    1. Refer to ISA 230 for a more complete list of documentation required.
    2. Planning (ISA 300) is a continual and iterative process throughout the audit.
    3. RMM = Risks of material misstatement.
    1. 关于所需文件的更完整清单,请参考《国际审计准则》第230条。
    2. 规划(ISA 300)是整个审计过程中一个持续的、反复的过程。
    3. RMM = 重大错报的风险。

    An effective risk assessment phase would include the following.

    Up-Front Involvement of Senior Team Members

    The engagement partner and other key members of the engagement team need to be actively involved in planning the audit, and in planning and participating in the discussion among engagement team members.

    This will ensure the audit plan takes advantage of their experience and insight.

    Note that ISAs usually refer to the term “auditor” as the person(s) performing the engagement.

    Where an ISA intends a requirement or responsibility be fulfilled by the engagement partner, the term “engagement partner” rather than “auditor” is used.

    An Emphasis on “Professional Skepticism”

    The auditor cannot be expected to disregard past experience of the honesty and integrity of the entity’s management and those charged with governance.

    Nevertheless, a belief that management and those charged with governance are honest and have integrity does not relieve the auditor of the need to maintain professional skepticism, or allow the auditor to be satisfied with less-than-persuasive audit evidence when obtaining reasonable assurance.

    Planning

    The time spent in audit planning (developing the overall audit strategy and audit plan) will ensure that audit objectives are properly met, and that the work of audit staff is always focused on gathering evidence on the most critical areas of potential misstatement.

    Team Discussions and Ongoing Communication

    A team planning discussion/meeting with the engagement partner present provides an excellent forum for:

    • Informing staff about the client in general and discussing potential risk areas;
    • Discussing the effectiveness of the overall audit strategy and the audit plan and then making changes as necessary;
    • Brainstorming how fraud could occur and then designing an appropriate response;
    • Discussing disclosures where there are higher risks of material misstatement; and
    • Allocating audit responsibilities and setting time frames.

    Ongoing communication among the audit team throughout the engagement is also important, for example discussing and addressing audit issues, unusual activities or possible indicators of fraud.

    This will enable timely communications to management and, where necessary, changes to the audit strategy and audit procedures.

    Focus on Risk Identification

    The most important step in a risk assessment process is to identify all the relevant risks.

    If business and fraud risk factors are not identified by the auditor, they will not be assessed or documented, and an appropriate audit response will not be designed.

    This is why well-designed risk assessment procedures are so important to the effectiveness of the audit.

    These risk assessment procedures also need to be performed by the appropriate level of staff.

    Financial Statement Disclosures

    In assessing risks, disclosures in the financial statements are also taken into account.

    Disclosures in the financial statements of SMEs may be less detailed or less complex (for example, some financial reporting frameworks allow smaller entities to provide fewer disclosures in their financial statements).

    However this does not relieve the auditor of the responsibility to obtain an understanding of disclosures and assess the risks of material misstatement in disclosures that are required.

    Ability to Evaluate Management’s Response(s) to Risk

    A key step in the risk assessment process is to evaluate the effectiveness of management’s responses (that is, management’s control design/implementation), if any, to mitigate the identified risks of material misstatement in the financial statements.

    In smaller entities, more reliance will likely be placed on the control environment (such as the competence and integrity of managements, etc.) and less on the traditional control activities (such as segregation of duties, etc.).

    Use of Professional Judgment

    The ISA audit requirements require the use and then documentation of significant judgments made by the auditor throughout the audit.

    Typical examples of tasks throughout the risk assessment process include:

    • Deciding to accept or continue with the client;
    • Developing the overall audit strategy;
    • Establishing materiality;
    • Assessing risks of material misstatement, including the identification of significant risks and other areas where special audit consideration may be necessary; and
    • Developing expectations for use when performing analytical procedures.

    一个有效的风险评估阶段将包括以下内容:

    高级团队成员的前期参与

    参与合伙人和参与团队的其他主要成员需要积极参与审计计划,并计划和参与参与团队成员之间的讨论。

    这将确保审计计划能够利用他们的经验和洞察力。

    请注意,《国际审计准则》中的 “审计师 “通常指的是执行审计工作的人。

    如果《国际审计准则》打算由参与伙伴履行一项要求或责任,则使用 “项目合伙人” (“engagement partner”) 而不是 “审计师 “一词。

    强调 “专业怀疑精神”

    不能指望审计师无视实体的管理层和负责管理的人过去的诚实和正直的经验。

    然而,相信管理层和负责管理的人是诚实和正直的,并不能免除审计师保持专业怀疑态度的需要,或允许审计师在获得合理保证时满足于不太有说服力的审计证据。

    规划

    花在审计规划(制定整体审计策略和审计计划)上的时间将确保审计目标得到适当满足,并确保审计人员的工作始终集中在收集潜在错报的最关键领域的证据上。

    团队讨论和持续沟通

    有业务伙伴在场的团队计划讨论/会议提供了一个很好的论坛。

    • 让员工了解客户的总体情况并讨论潜在的风险领域。
    • 讨论整体审计策略和审计计划的有效性,然后根据需要进行修改。
    • 集思广益,探讨欺诈如何发生,然后设计适当的应对措施。
    • 讨论存在较高重大错报风险的披露事项;以及
    • 分配审计责任并设定时间框架。

    在整个工作过程中,审计团队之间的持续沟通也很重要,例如,讨论和解决审计问题、异常活动或可能的欺诈迹象。

    这将有助于及时与管理层沟通,并在必要时改变审计策略和审计程序。

    专注于风险识别

    风险评估过程中最重要的一步是识别所有相关风险。

    如果审计师没有识别出业务和欺诈风险因素,就不会对其进行评估或记录,也就不会设计出适当的审计对策。

    这就是为什么精心设计的风险评估程序对审计的有效性如此重要。

    这些风险评估程序也需要由适当级别的工作人员执行。

    财务报表的披露

    在评估风险时,也要考虑到财务报表中的披露情况。

    中小企业的财务报表中的披露可能不那么详细或不那么复杂(例如,一些财务报告框架允许较小的实体在其财务报表中提供较少的披露)。

    然而,这并不免除审计师对披露内容的理解和评估所需披露内容的重大误报风险的责任。

    评估管理层对风险的反应的能力

    风险评估过程中的一个关键步骤是评价管理层的反应(即管理层的控制设计/实施)的有效性,如果有的话,以减轻财务报表中已识别的重大错报风险。

    在较小的实体中,可能会更依赖控制环境(如管理层的能力和诚信等),而较少依赖传统的控制活动(如职责分离等)

    专业判断的使用

    国际审计师协会的审计要求要求审计师在整个审计过程中使用并记录重要的判断。

    在整个风险评估过程中,典型的任务例子包括:-

    • 决定是否接受或继续与客户合作。
    • 制定整体的审计策略。
    • 确定重要性。
    • 评估重大错报的风险,包括识别重大风险和其他可能需要特别审计考虑的领域;以及
    • 制定预期,以便在执行分析程序时使用。

    Risk Response | 风险应对

    Notes:

    1. Refer to ISA 230 for a more complete list of documentation required.
    2. Planning (ISA 300) is a continual and iterative process throughout the audit.
    3. RMM = Risks of material misstatement.
    1. 关于所需文件的更完整清单,请参考《国际审计准则》第230条。
    2. 规划(ISA 300)是整个审计过程中一个持续的、反复的过程。
    3. RMM = 重大错报的风险。

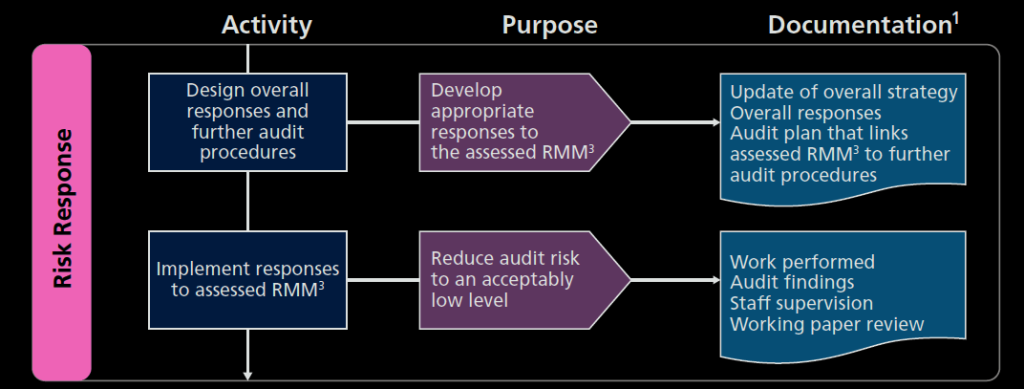
    In this phase, the auditor considers the reasons (inherent and control risks) for the risk assessments at the financial statement level and at the assertion level (for each class of transactions, event, account balance, and disclosure), and develops responsive audit procedures.

    The auditor’s response to the assessed risks of material misstatement is documented in an audit plan that:

    • Contains an overall response to the risks identified at the financial statement level;
    • Identifies the material financial statement areas and significant disclosures; and
    • Contains the nature, extent, and timing of specific audit procedures tailored to respond to the assessed risks of material misstatement at the assertion level.

    The overall responses address assessed risks of material misstatement at the financial statement level.

    Such responses would include the assignment and supervision of appropriate personnel, need for professional skepticism, the extent of corroboration required for management’s explanations/representations, consideration of the type of audit procedures to be performed, and what documentation would be examined in support of material transactions.

    Further audit procedures generally consist of substantive procedures such as tests of details, analytical procedures, and tests of controls (where there is an expectation that such controls have been operating effectively during the period).

    在此阶段,审计师考虑在财务报表层面和认定层面(针对每一类交易、事件、账户余额和披露)进行风险评估的原因(内在和控制风险),并制定响应的审计程序。

    审计师对评估的重大错报风险的反应记录在审计计划中,该计划包括

    • 包含对财务报表层面所确定的风险的总体回应。
    • 确定重大财务报表领域和重要披露;以及
    • 包含具体审计程序的性质、范围和时间,以应对评估的认定层面的重大错报风险。
    • 总体应对措施涉及财务报表层面的评估的重大错报风险。

    这种反应将包括指派和监督适当的人员,专业怀疑的需要,管理层的解释/陈述所需的确证程度,考虑要执行的审计程序的类型,以及将检查哪些文件以支持重大交易。

    进一步的审计程序通常包括实质性程序,如细节测试、分析性程序和控制测试(如果预期这种控制在该期间有效运行)。

    Some of the matters the auditor should consider when planning the appropriate mix of audit procedures to respond to identified risks include the following:

    审计员在计划适当的审计程序组合以应对已确定的风险时,应考虑的一些事项包括:

    Use of tests of controls

    • Identify relevant internal controls that, if tested, would reduce the need/scope for other substantive procedures.
      • As a general rule, the sample size for testing controls is often significantly less than that of a substantive test of a transaction stream.
      • Assuming that the relevant controls operate consistently and control deviations are unlikely, the use of tests of controls can often result in less work being performed.
      • However, there is no requirement that the operating effectiveness of internal controls (direct or indirect) be tested.
    • Identify any assertions that cannot be addressed by substantive procedures alone. For example, this can often apply to completeness of sales in a small entity, and situations where there is highly automated processing of transactions (such as Internet sales) with little or no manual intervention.

    对控制的测试的使用

    • 识别相关的内部控制,如果进行测试,将减少其他实质性程序的需要/范围。
      • 作为一般规则,测试控制的样本量往往大大低于对交易流的实质性测试。
      • 假设相关控制措施的运行是一致的,并且控制措施的偏差不太可能发生,使用控制措施的测试往往可以减少执行的工作。
      • 然而,没有要求对内部控制(直接或间接)的运行有效性进行测试。
    • 识别任何不能仅通过实质性程序解决的认定。例如,这往往适用于小型实体的销售完整性,以及交易的高度自动化处理(如互联网销售),很少或没有人工干预的情况。

    Substantive Analytical Procedures

    These are procedures for which the total amount of a transaction stream can be reliably predicted based on available evidence.

    This expectation is compared to the actual amount in the accounting records, and the extent of any misstatement readily identified.

    In some cases, if the assessed risk for a particular assertion is low (without considering related controls), the auditor may determine that substantive analytical procedures alone would provide sufficient appropriate audit evidence.

    实质性分析程序

    这些程序是指根据现有的证据,可以可靠地预测交易流的总金额。

    这种预测与会计记录中的实际金额进行比较,并随时确定任何错报的程度。

    在某些情况下,如果对某一特定认定的评估风险较低(不考虑相关控制),审计师可以确定仅实质性分析程序就能提供足够的适当审计证据。

    Unpredictability

    The need to incorporate an element of unpredictability in procedures performed, such as when responding to a risk of material misstatement due to possible fraud.

    For example, visits to inventory count locations could be unannounced or certain procedures could be carried out prior to the year-end that are unannounced.

    Unpredictability also needs to be considered in how much information is provided to management with regard to planned audit procedures and their timing.

    不可预测性

    需要在执行的程序中加入不可预测的因素,例如,在应对可能的欺诈导致的重大错报风险时。

    例如,对存货清点地点的访问可以不事先通知,或者在年终前进行某些程序,但不事先通知。

    在向管理层提供多少有关计划中的审计程序及其时间的信息时,也需要考虑到不可预测性。

    Management override

    The need for specific audit procedures to address the potential for management override.

    Significant risks

    The audit response to “significant risks” that have been identified.

    管理部门的控制权

    需要制定具体的审计程序,以解决管理层凌驾的可能性。

    重大风险

    对已确定的 “重大风险 “的审计反应。

    Reporting | 报告

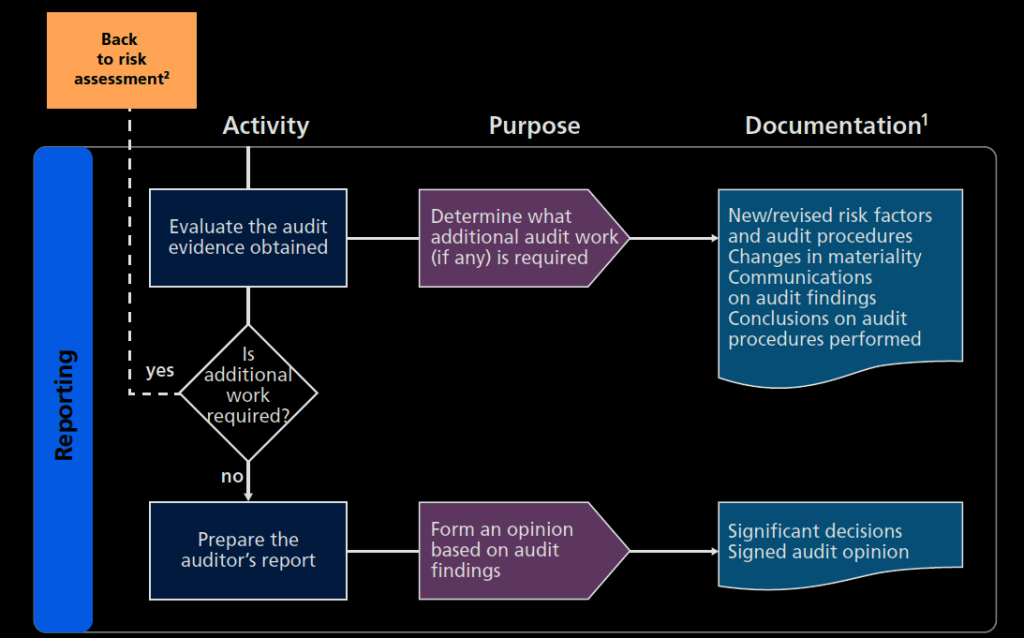
    Notes:

    1. Refer to ISA 230 for a more complete list of documentation required.
    2. Planning (ISA 300) is a continual and iterative process throughout the audit.
    1. 关于所需文件的更完整清单,请参考《国际审计准则》第230条。
    2. 规划(ISA 300)是整个审计过程中一个持续的、反复的过程。

    The final phase of the audit is to assess the audit evidence obtained and determine whether it is sufficient and appropriate to reduce audit risk to an acceptably low level.

    It is important during this phase of the audit to determine:

    • Any change in the assessed level of risk;
    • Whether conclusions drawn from the work performed are appropriate;
    • If any suspicious circumstances have been encountered; and
    • That additional risks (not previously identified) have been appropriately assessed and further audit procedures performed as required.

    A team debriefing meeting (towards or at the end of the fieldwork) is not a specific requirement of the ISAs, but can be useful for staff to discuss the audit findings, identify any indications of fraud, and determine the need (if any) to perform any further audit procedures.

    When all procedures have been performed and conclusions reached:

    • Audit findings should be reported to management and those charged with governance; and
    • An audit opinion should be formed and a decision made on the appropriate wording for the auditor’s report.

    审计的最后阶段是评估所获得的审计证据,并确定其是否充分和适当,以将审计风险降低到可接受的低水平。

    在这一阶段的审计工作中,重要的是要确定:

    • 评估的风险水平的任何变化。
    • 从所进行的工作中得出的结论是否适当。
    • 是否遇到了任何可疑的情况;以及
    • 额外的风险(以前没有确定)已经得到适当的评估,并根据需要执行进一步的审计程序。

    团队汇报会议(在实地工作即将结束时或结束时)并不是《国际审计准则》的具体要求,但对于工作人员讨论审计结果、识别任何欺诈迹象以及确定是否需要(如果有的话)执行任何进一步的审计程序来说是有用的。

    当所有程序都已执行并得出结论时:-

    • 应将审计结果报告给管理层和负责管理的人;以及
    • 应形成审计意见,并就审计报告的适当措辞做出决定。
    Our website's articles, templates, and material are solely for you to look over. Although we make every effort to keep the information up to date and accurate, we make no representations or warranties of any kind, either express or implied, regarding the website or the information, articles, templates, or related graphics that are contained on the website in terms of its completeness, accuracy, reliability, suitability, or availability. Therefore, any reliance on such information is strictly at your own risk.

    Keep in touch with us so that you can receive timely updates |

    要获得即时更新,请与我们保持联系

    1. Website ✍️ https://www.ccs-co.com/ 2. Telegram ✍️ http://bit.ly/YourAuditor 3. Facebook ✍

    4. Blog ✍ https://lnkd.in/e-Pu8_G 5. Google ✍ https://lnkd.in/ehZE6mxy

    6. LinkedIn ✍ https://www.linkedin.com/company/74734209/admin/
    12
  • Audit Documentation

    Audit Documentation

    Sufficient audit documentation is required to enable an experienced auditor, having no previous connection with the audit, to understand:

    • The nature, timing, and extent of the audit procedures performed;
    • The results of performing those procedures and the audit evidence obtained; and
    • Significant matters arising during the audit, the conclusions reached thereon; and significant professional judgments made in reaching those conclusions.

    Audit documentation for a smaller entity is generally less extensive than that for the audit of a larger entity.

    For example, various aspects of the audit could be recorded together in a single document, with cross-references to supporting working papers, as appropriate.

    It is not necessary for the auditor to document:

    • Every minor matter considered, or every professional judgment made, in an audit; and
    • Compliance with matters for which compliance is demonstrated by documents included within the audit file. For example, an audit plan on file demonstrates that the audit was planned, and a signed engagement letter demonstrates that the auditor has agreed to the terms of the audit engagement.

    需要有足够的审计文件,以使之前与相关审计无关的有经验审计师能够理解到:

    • 所执行的审计程序的性质、时间和范围。
    • 执行这些程序的结果和获得的审计证据;以及
    • 审计过程中出现的重大事项,就此得出的结论;以及在得出这些结论时作出的重大专业判断。

    小型实体的审计文件通常没有大型实体的审计文件广泛。

    例如,审计的各个方面可以一起记录在一份文件中,并酌情交叉引用辅助工作文件。

    审计师也没有必要记录:-

    • 在审计中所考虑的每一个小问题,或做出的每一个专业判断;以及
    • 在审计档案中包含的文件所证明的事项的合规性。例如,档案中的审计计划表明审计是有计划的,签署的业务约定书表明审计师已同意审计业务的条款。
    Our website's articles, templates, and material are solely for you to look over. Although we make every effort to keep the information up to date and accurate, we make no representations or warranties of any kind, either express or implied, regarding the website or the information, articles, templates, or related graphics that are contained on the website in terms of its completeness, accuracy, reliability, suitability, or availability. Therefore, any reliance on such information is strictly at your own risk.

    Keep in touch with us so that you can receive timely updates |

    要获得即时更新,请与我们保持联系

    1. Website ✍️ https://www.ccs-co.com/ 2. Telegram ✍️ http://bit.ly/YourAuditor 3. Facebook ✍

    4. Blog ✍ https://lnkd.in/e-Pu8_G 5. Google ✍ https://lnkd.in/ehZE6mxy

    6. LinkedIn ✍ https://www.linkedin.com/company/74734209/admin/
    10
  • Benefits of the Risk-Based Audit

    Benefits of the Risk-Based Audit

    Some of the benefits of the risk-based approach are summarised in the exhibit below.

    风险导向性审计方法(risk-based approach)进行审计的一些好处在下面的展览中进行了总结。

    Time Flexibility When Audit Work Needs to Be Performed

    Because risk assessment procedures do not involve the detailed testing of transactions and balances, they can be performed well before the period end, assuming no major operational changes are anticipated.

    This can help in balancing the workload of audit staff more evenly throughout the period.

    It may provide the client with time to respond to identified (and communicated) weaknesses in internal control and other requests for assistance before the commencement of period-end audit fieldwork.

    However, where interim financial information is not readily available, the analytical risk assessment procedures may have to be performed at a later date.

    需要进行审计工作时的时间灵活性

    由于风险评估程序不涉及交易和余额的详细测试,因此,假设没有重大的业务变化,它们可以在期末前很早就执行。

    这可以帮助平衡审计人员在整个期间的工作量,使其更加均匀。

    它可以为客户提供时间,在期末审计工作开始前,对已发现的(和通报的)内部控制的弱点和其他援助要求作出回应。

    然而,如果中期财务信息不是现成的,分析性风险评估程序可能必须在晚些时候进行。

    Audit Team’s Effort Focused on Key Areas

    By understanding where the risks of material misstatement can occur in financial statements, the auditor can direct the audit team’s effort toward high-risk areas and perhaps reduce work in lower-risk areas.

    This will also help to ensure that audit staff resources are used effectively.

    审计小组的工作集中在关键领域

    通过了解财务报表中可能发生重大错报的风险,审计师可以将审计小组的工作引向高风险领域,或许可以减少低风险领域的工作。

    这也将有助于确保审计人员的资源得到有效利用。

    Audit Procedures Focused on Specific Risks

    Further audit procedures are designed to respond to assessed risks.

    Consequently, tests of details that only address risks in general terms may be significantly reduced or even eliminated.

    专注于特定风险的审计程序

    进一步的审计程序是为了应对评估的风险而设计的。

    因此,只针对一般风险的细节测试可能会大大减少,甚至取消。

    Understanding of Internal Control

    The required understanding of internal control enables the auditor to make informed decisions on whether to test the operating effectiveness of internal control.

    Tests of controls (for which some controls may only require testing every three years) will often result in much less work being required than performing extensive tests of details.

    对内部控制的理解

    对内部控制的必要了解使审计师能够就是否测试内部控制的运行效果做出明智的决定。

    对控制的测试(有些控制可能只需要每三年测试一次)往往会比对细节进行广泛的测试所需的工作要少很多。

    Timely Communication of Matters of Interest to Management

    The improved understanding of internal control may enable the auditor to identify weaknesses in internal control (such as in the control environment and general IT controls) that were not previously recognised.

    Communicating these weaknesses to management on a timely basis will enable them to take appropriate action, which is to their benefit.

    This may also save time in performing the audit.

    及时向管理层传达感兴趣的事项

    对内部控制理解的提高可能会使审计师发现以前没有认识到的内部控制的弱点(如控制环境和一般IT控制)。

    将这些弱点及时传达给管理层,将使他们能够采取适当的行动,这对他们是有利的。

    这也可以节省执行审计的时间。

    Our website's articles, templates, and material are solely for you to look over. Although we make every effort to keep the information up to date and accurate, we make no representations or warranties of any kind, either express or implied, regarding the website or the information, articles, templates, or related graphics that are contained on the website in terms of its completeness, accuracy, reliability, suitability, or availability. Therefore, any reliance on such information is strictly at your own risk.

    Keep in touch with us so that you can receive timely updates |

    要获得即时更新,请与我们保持联系

    1. Website ✍️ https://www.ccs-co.com/ 2. Telegram ✍️ http://bit.ly/YourAuditor 3. Facebook ✍

    4. Blog ✍ https://lnkd.in/e-Pu8_G 5. Google ✍ https://lnkd.in/ehZE6mxy

    6. LinkedIn ✍ https://www.linkedin.com/company/74734209/admin/
    14
  • ISAs for Smaller Audits

    ISAs for Smaller Audits

    ISAs do not distinguish the audit approach required for a one-person entity from that required for a multinational entity employing thousands of people.

    An audit is an audit.

    Consequently, the basic approach to an audit does not change just because the entity is small.

    The word “audit” is intended to convey a clear message to users of financial statements.

    That message is that the auditor has obtained reasonable assurance that the financial statements are free from material misstatements, regardless of the size or type of the entity that has been audited.

    对一个人的实体所要求的审计方法和对一个雇用数着千人的跨国实体所要求的审计方法,《国际审计准则》并没有去作出区分。

    审计就是审计。

    因此,审计的基本方法并不因为实体的规模小而改变。

    “审计”一词的目的是向财务报表的使用者传达一个明确的信息。

    这个信息就是,无论被审计的实体的规模或类型如何,审计师已经获得了财务报表不存在重大错报的合理保证。

    This issue of proportionality was addressed by IAASB staff in a Staff Questions and Answers document, entitled Applying ISAs Proportionately with the Size and Complexity of an Entity, issued in August 2009.

    Its purpose is to assist auditors in applying the clarified ISAs in a cost-effective manner.

    IAASB 工作人员在2009年8月发布的题为《根据实体的规模和复杂性适度应用国际审计准则》的工作人员问答文件中讨论了这个比例问题。

    其目的是协助审计师以具有成本效益的方式应用明晰化 (Clarity) 的国际审计准则。

    The response to the question “How do the ISAs address the fact that the characteristics of an SME are significantly different from those of a larger, more complex entity” was as follows:

    对于”中小企业与更大、更复杂的实体的特点有很大不同,《国际审计准则》要如何处理这一问题”,答复如下:

    “The auditor’s objectives are the same for audits of entities of different sizes and complexities.

    This, however, does not mean that every audit will be planned and performed in exactly the same way.

    The ISAs recognise that the specific audit procedures to be undertaken to achieve the auditor’s objectives and to comply with the requirements of the ISAs may vary considerably depending on whether the entity being audited is large or small and whether it is complex or relatively simple.

    “对于不同规模和复杂程度的实体的审计,审计师的目标是相同的。

    然而,这并不意味着每项审计都将以完全相同的方式进行计划和实施。

    《国际审计准则》认识到,为实现审计师的目标和遵守《国际审计准则》的要求而采取的具体审计程序可能会因被审计的实体是大是小,是复杂还是相对简单而有很大的不同。

    The requirements of the ISAs, therefore, focus on matters that the auditor needs to address in an audit and do not ordinarily detail the specific procedures that the auditor should perform.

    The ISAs also explain that the appropriate audit approach for designing and performing further audit procedures depends on the auditor’s risk assessment.

    For example, based on the required understanding of the entity and its environment, including its internal control and the assessed risks of material misstatement, the auditor may determine that a combined approach using both tests of controls and substantive procedures is an effective approach in the circumstances in responding to the assessed risks.

    因此,《国际审计准则》的要求侧重于审计师在审计中需要处理的事项,通常不详细说明审计师应执行的具体程序。

    《国际审计准则》还解释说,设计和执行进一步审计程序的适当审计方法取决于审计师的风险评估。

    例如,根据对该实体及其环境的必要了解,包括其内部控制和评估的重大错报风险,审计师可以确定,在这种情况下,使用控制测试和实质性程序的综合方法是应对评估风险的有效方法。

    In other cases, for example, in the context of an SME audit where there are not many control activities in the SME that can be identified by the auditor, the auditor may decide that it is efficient to perform further audit procedures that are primarily substantive procedures.

    It is also important to note that the ISAs acknowledge that the appropriate exercise of professional judgment is essential to the proper conduct of an audit.

    Professional judgment is necessary, in particular, regarding decisions about the nature, timing, and extent of audit procedures used to meet the requirements of the ISAs and gather audit evidence.

    在其他情况下,例如,在中小企业审计中,审计师可以确定的中小企业的控制活动不多,审计师可以决定有效地执行

    进一步的审计程序,主要是实质性程序。

    同样重要的是要注意,《国际审计准则》承认,适当地行使专业判断对于正确地进行审计是至关重要的。

    专业判断是必要的,特别是在决定审计程序的性质、时间和范围方面。

    专业判断是必要的,特别是关于用于满足《国际审计准则》的要求和收集审计证据的审计程序的性质、时间和范围的决定。

    However, while the auditor of an SME needs to exercise professional judgment, this does not mean that the auditor can decide not to apply a requirement of an ISA except in exceptional circumstances and provided that the auditor performs alternative audit procedures to achieve the aim of the requirement.”

    然而,虽然中小企业的审计师需要进行专业判断,但这并不意味着审计师可以决定不适用《国际审计准则》的某项要求,除非在特殊情况下,并且审计师执行替代的审计程序以实现该要求的目的。”

    The key points in the excerpt above can be summarised as follows:

    • Audit objectives are the same for any size of audit;
    • The specific audit procedures required may vary considerably depending on the size of entity and the assessed risks;
    • The ISAs focus on matters the auditor needs to address — not on the details of specific procedures;
    • The design of further audit procedures depends on the auditor’s risk assessment;
    • The appropriate exercise of professional judgment is essential in tailoring the procedures to respond appropriately to the assessed risks; and
    • Professional judgment cannot be used to avoid compliance with any ISA requirements except in exceptional circumstances.

    上述摘录中的关键点可以概括为以下几点:-

    • 审计目标对于任何规模的审计都是一样的。
    • 所需的具体审计程序可能有很大的不同,这取决于实体的规模和所需的具体审计程序可能会有很大的不同,这取决于实体的规模和评估的风险。
    • 《国际审计准则》的重点是审计师需要处理的事项–而不是具体程序的细节。
    • 进一步审计程序的设计取决于审计师的风险评估。
    • 适当行使专业判断对于调整程序以适当应对评估的风险至关重要;以及
    • 除非在特殊情况下,不能用专业判断来避免遵守《国际审计准则》的任何要求。

    Some suggestions | 一些建议

    In addition, the ISAs contain a number of paragraphs that address considerations specific to audits of SMEs.

    Some suggestions for successfully implementing ISAs on smaller engagements are included below.

    此外,《国际审计准则》包含一些段落,涉及对中小企业审计的具体考虑。

    以下是关于在较小的业务中成功实施国际审计准则的一些建议。

    1. Take time to read the clarified ISAs and to train staff

    Failure to understand the requirements can lead to:

    • The entire risk assessment phase of the audit becoming an “add-on” to the other substantive audit work performed.
      • It should be the risk assessment that drives the selection of audit procedures to be performed, not a standardised listing of procedures that could be applied to any entity.
      • The purpose of the risk assessment is to focus the audit effort on areas where there is a greater risk of material misstatement in the financial statements, and away from less risky areas.
    • Turning what should be a simple audit into a complex and time-consuming project. This can arise if efforts are focused on completing needless standard audit forms and checklists, rather than using professional judgment to scale the work according to the size and complexity of the entity being audited and the risks involved.
    • Failure to comply with an ISA (“the auditor shall”) requirement.

    1. 花时间阅读澄清后的《国际审计准则》并培训员工。

    不了解这些要求会导致:-

    • 整个审计的风险评估阶段成为其他实质性审计工作的 “附加 “部分。
      • 应该由风险评估来推动对要执行的审计程序的选择,而不是对任何实体适用的程序的标准化清单。
      • 风险评估的目的是将审计工作集中在财务报表中存在较大的重大错报风险的领域,而不是风险较小的领域。
    • 将本应是简单的审计变成复杂而耗时的项目。如果把精力集中在完成不必要的标准审计表格和核对表上,而不是根据被审计单位的规模和复杂性以及所涉及的风险,利用专业判断来调整工作,就会出现这种情况。
    • 未能遵守国际审计准则(”审计师应”)的要求。

    2. Take time to plan well, no matter how small the engagement

    It has been said an hour spent in planning can save many more in execution.

    Effective audit planning is often the difference between a quality audit within budget and a poor-quality audit that goes over budget.

    This does not necessarily mean holding dedicated team meetings in the office.

    On very small engagements, planning can be achieved through brief discussions at the start of the engagement and as the audit progresses.

    Key areas to address in planning:-

    • Encourage staff to identify areas where the usual audit procedures seem excessive in relation to the risk of misstatement being addressed.
    • Take time to ensure that each staff member understands the necessity and purpose of the documentation he or she is required to complete. Countless hours can be lost by staff attempting to complete forms they do not understand.
    • Discuss the potential for fraud. Encourage staff to be skeptical and inquisitive, and empower them to raise issues, observations, or unexplained matters.
    • Discuss known related parties and the nature/size of transactions.
    • Consider whether the audit documentation prepared in previous periods can simply be updated for changes that have occurred, rather than be prepared all over again. Documentation and assessment of risk factors and relevant internal controls should be sufficient to enable auditors in subsequent periods to leverage their understanding of the entity and focus attention on new industry trends, key operational changes, new inherent risks, and revised internal controls.

    2. 花时间做好计划,无论工作有多小

    有人说,花在计划上的一小时可以在执行上节省更多。

    有效的审计计划往往是预算内高质量审计和超出预算的低质量审计之间的区别。

    这并不一定意味着在办公室里举行专门的团队会议。

    在非常小的审计项目中,计划可以通过以下方式实现在很小的项目中,可以通过在项目开始时和审计进展中的简短讨论来实现规划。

    规划中需要解决的关键领域:-

    • 鼓励员工找出通常的审计程序与所处理的错报风险相比似乎过多的领域。
    • 花时间确保每个工作人员了解他或她需要完成的文件的必要性和目的。由于工作人员试图填写他们不理解的表格,可能会损失无数的时间。
    • 讨论欺诈的可能性。鼓励员工持怀疑态度和好奇心,并授权他们提出问题、意见或无法解释的事项。
    • 讨论已知的关联方和交易的性质/规模。
    • 考虑是否可以简单地更新以前时期准备的审计文件,以适应已经发生的变化,而不是重新准备。对风险因素和相关内部控制的文件和评估应足以使审计人员在随后的时期利用他们对该实体的理解,将注意力集中在新的行业趋势、关键的业务变化、新的固有风险和修订的内部控制上。

    3. Evaluate the control environment

    Take time to understand the pervasive internal controls that are part of the control environment.

    Pervasive controls are quite different from transactional controls; they address such matters such as integrity and ethics, corporate governance, employee competence, management’s attitudes toward control, fraud prevention, risk management, and control monitoring.

    If the “tone at the top” is poor, management override can easily occur, and even the very best transactional controls over processes such as purchases and sales could be undermined.

    3. 评估控制环境

    花时间了解作为控制环境一部分的普遍性内部控制。

    普遍性控制与交易性控制截然不同;它们涉及诸如诚信和道德、公司治理、员工能力、管理层对控制的态度、欺诈预防、风险管理和控制监测等事项。

    如果 “高层的基调 “不好,就很容易发生管理层凌驾于人之上的情况,即使是对采购和销售等过程的最好的交易控制也会被破坏。

    4. Aim for continual improvement

    There is a tendency for some auditors to blindly follow the example of the previous auditor, resulting in a file that mirrors that of the previous year. A much better approach is to continually review/challenge the work performed in previous years, and identify changes that will make the audit more efficient and effective.

    4. 以持续改进为目标

    有些审计师倾向于盲目地效仿前任审计师的做法,导致文件与前一年的情况如出一辙。

    一个更好的方法是不断审查/挑战前几年的工作,并确定能使审计更有效率和效果的变化。

    Our website's articles, templates, and material are solely for you to look over. Although we make every effort to keep the information up to date and accurate, we make no representations or warranties of any kind, either express or implied, regarding the website or the information, articles, templates, or related graphics that are contained on the website in terms of its completeness, accuracy, reliability, suitability, or availability. Therefore, any reliance on such information is strictly at your own risk.

    Keep in touch with us so that you can receive timely updates |

    要获得即时更新,请与我们保持联系

    1. Website ✍️ https://www.ccs-co.com/ 2. Telegram ✍️ http://bit.ly/YourAuditor 3. Facebook ✍

    4. Blog ✍ https://lnkd.in/e-Pu8_G 5. Google ✍ https://lnkd.in/ehZE6mxy

    6. LinkedIn ✍ https://www.linkedin.com/company/74734209/admin/
    13